
Drive sharing permissions determine who can view, comment on, or edit a file based on their role, the folder it lives in, and any policies your organization sets. Before changing anything, check whether the item inherits access from a parent folder, since that's where most sharing problems start. When in doubt, set general access to Restricted and work from there. Keep two models in mind: My Drive roles for personal files and Shared Drive roles for team-owned content.
TL;DR:
- Files inherit their parent folder’s permissions, so removing someone from an individual file will not revoke access granted by that folder or its groups.
- Owners can restrict editors from changing permissions or resharing, and can block viewers and commenters from downloading, printing, or copying files.
- Shared Drive files remain owned by the organization when members leave, while Managers control membership and admins can limit external sharing or downloads.
- Visitors verify by email PIN, but access expires after seven days without reverification, and they cannot join a Shared Drive at its root.
- When access persists, check group membership, general access links, parent folders, and Shared Drive membership, then test with another account.
Table of Contents
- My Drive Permission Roles and What Each One Can Do
- How Folder Permission Inheritance Shapes Access
- Step-by-Step: Setting, Changing, and Stopping Sharing
- Shared Drive Roles and How They Change Governance
- Admin Controls and Org-Level Sharing Policies
- Visitor, Guest, and External Sharing Limits
- Troubleshooting: Why Someone Still Has Access
- Quick Checklist to Reduce Accidental Over-Sharing
- What I've Learned Fixing Access Problems
- Where Semester Flow Fits Alongside Drive Permissions
- FAQ
- Sources
My Drive Permission Roles and What Each One Can Do
My Drive has four roles, and the differences matter more than most people realize. A Viewer can open and download a file but not change it. A Commenter can add comments and suggestions without touching the actual content. An Editor can change the file, rename it, and in many cases reshare it with others. The Owner controls everything, including who else can be an owner.
- Viewer: opens, downloads, and copies the file, nothing else.
- Commenter: does everything a Viewer does, plus leaves comments and suggested edits.
- Editor: edits content, and by default can add or remove other people and change their roles.
- Owner: transfers ownership, deletes the file, and overrides any permission set by an editor.
Owners aren't stuck with an editor's default reach. According to Google's sharing instructions, owners can turn off an editor's ability to change permissions or share the file further, and can also block viewers and commenters from downloading, printing, or copying. Some accounts also support expiration dates on shared links, which is worth using for anything time-sensitive like a shared draft or a temporary collaborator invite.
How Folder Permission Inheritance Shapes Access
Folders, not individual files, are the real access boundary in Google Drive. Every file or subfolder placed inside a folder inherits that folder's permissions automatically, and new files added later pick up the same access as everything around them. This is useful until it isn't: you cannot give one file inside a folder less access than the folder itself grants, because the parent's permission level sets the floor for everything underneath it.
- A file moved into a shared folder instantly gains that folder's access list.
- Removing a person from a single file does nothing if they still have access through the parent folder.
- A limited-access subfolder, created specifically with a narrower sharing list, is the only way to carve out a more restricted zone inside a broader share.
Say a professor shares a course folder with an entire class, then needs to share one file only with three students. Moving that file into a new subfolder with its own, smaller sharing list is the fix, not trying to edit the file's permissions directly while it sits inside the open folder. This pattern is confirmed in Google's folder sharing guide, which recommends limited-access subfolders whenever a narrower boundary is required.
Pro Tip: Treat the folder, not the file, as your access control. Fix the boundary at the folder level and the files inside it will follow.

Step-by-Step: Setting, Changing, and Stopping Sharing
Changing permissions in Drive follows the same basic pattern whether you're working with a single file or an entire folder.
- Select the file or folder, right-click, and choose Share.
- Under "Share with people and groups," add an email address or group, then pick Viewer, Commenter, or Editor from the dropdown.
- Under "General access," choose Restricted to limit access to people added individually, or choose an option that generates a link if broader access is intended.
- Click Send or Done to apply the change.
- To stop sharing with a specific person, open Share again, find their name under "People with access," and remove them or change their role.
To stop sharing entirely, set general access to Restricted and remove individual collaborators one by one. One catch worth flagging: according to Google's guidance on stopping or changing sharing, changing a child item's general access to Restricted does not remove access that someone already has through a parent folder. If a person still sees the file after you've "removed" them, the parent folder is almost always why.
Owners can also turn off an editor's ability to change permissions, download, print, or copy a file, a setting found in the same Share dialog under the advanced sharing options. For anyone building integrations or automated workflows, note that the required roles differ between My Drive and Shared Drives: the Drive API's sharing documentation specifies writer and reader roles for My Drive but organizer and fileOrganizer roles for Shared Drives, so a script written for one won't necessarily behave correctly on the other.
One access path, multiple causes: a file can show "shared" for reasons tied to groups, links, or inheritance rather than a direct share, which is why testing effective access matters more than trusting the share list on its face, per Google's guide to how Drive access is calculated.
Shared Drive Roles and How They Change Governance
Shared Drives work differently from My Drive because files belong to the organization, not to any individual member. That single difference changes almost everything about how access should be managed.
- Manager: full control, including adding or removing members and changing Shared Drive settings.
- Content manager: edits, moves, and organizes content but can't change membership.
- Contributor: adds and edits files without reorganizing the drive's structure.
- Commenter: comments only, no editing.
- Viewer: views and downloads, nothing more.
Because the organization owns every file, content persists when a member leaves, which solves the classic problem of a departing employee taking critical files with them. According to Google's setup guide for Shared Drives, administrators and managers can also set drive-level sharing settings, including whether content managers can share folders outside the drive, whether members can share with people outside the organization, and whether files can be downloaded, printed, or copied by viewers and commenters.
Admin Controls and Org-Level Sharing Policies
Workspace admins hold levers that sit above individual file and folder settings, and those policies can override what an owner or manager tries to configure at the item level.
- Organizational unit defaults that set the baseline general-access setting for everyone in a group.
- Allow or deny toggles for external sharing, both outbound and inbound.
- Visitor sharing toggles that control whether non-Google-account collaborators can be invited at all.
- Settings that determine whether individual managers can override the org-wide defaults for their own Shared Drives.
Trust rules and target audiences add another layer: these let an admin define which domains or groups are treated as "trusted" for sharing purposes, which in turn changes what general-access options appear in the Share dialog for end users. The practical admin workflow is to check Manage shared drives regularly, confirm which org units allow manager overrides, and keep Restricted as the recommended default wherever sensitive material is involved, a recommendation echoed in Google's admin-level sharing documentation.
Pro Tip: Review org-unit sharing defaults quarterly, not just when a security incident forces the question.
Visitor, Guest, and External Sharing Limits
Visitor sharing lets someone without a Google account collaborate using email-based PIN verification, but that access typically expires after seven days unless they reverify. Visitors can view, comment, or edit depending on the role granted, but they can never own a file and cannot be added as a member of a Shared Drive at the root level.
- Visitors verify identity through a one-time PIN sent to their email.
- Access lapses after seven days without reverification, per Google's guide to sharing with people who don't have Google accounts.
- Admins can disable visitor sharing entirely at the org-unit level if non-account collaboration isn't acceptable for a given group.
Troubleshooting: Why Someone Still Has Access
When a person still has access after you thought you removed it, work through the actual access path rather than guessing.
- Open Manage access on the file and check every person and group listed, not just the names you recognize.
- Check whether a group the person belongs to has access, since removing them individually won't help if the group grants the same permission.
- Review the general-access link setting, since an "Anyone with the link" setting bypasses the named-people list entirely.
- Check Shared Drive membership and admin trust rules, since a drive-level setting can grant access that overrides what you set on a single file.
- Test with a different account or an incognito browser session logged in as the person in question, where possible, to confirm what they actually see.
- Group membership is one of the most common causes of "I removed them but they still have access."
- Inherited parent-folder permissions are the second most common cause.
- A general-access link set to anything other than Restricted overrides individual removals.
The fix is almost always to change access at the source: remove the person from the group, adjust the parent folder's sharing list, or change the Shared Drive setting, rather than repeatedly editing the child file.
Quick Checklist to Reduce Accidental Over-Sharing
A short monthly routine prevents most sharing mistakes before they become problems.
- Set general access to Restricted by default and review link-sharing settings monthly.
- Use Shared Drives for team-owned content and keep the Manager role limited to a small group.
- Create limited-access subfolders for sensitive files instead of trying to restrict individual items inside an open folder.
- When someone leaves a team, audit their group memberships and any links they created before closing out their account.
Pro Tip: Document each shared folder's purpose and owner so the next audit takes minutes instead of hours.
What I've Learned Fixing Access Problems
The fix is almost always the same: audit the parent folder, move sensitive files into a limited-access subfolder, revoke the group membership causing the leak, then retest with a different account. Folders are the boundary that matters, and automating that audit saves hours every semester.
— Haden
Where Semester Flow Fits Alongside Drive Permissions
Drive permissions handle who can see a file. Keeping course material organized in the first place is a separate problem, and that's where Semester Flow comes in: we parse uploaded syllabi, extract deadlines automatically, and sync everything to Google Calendar so students aren't manually sorting folders during midterms.
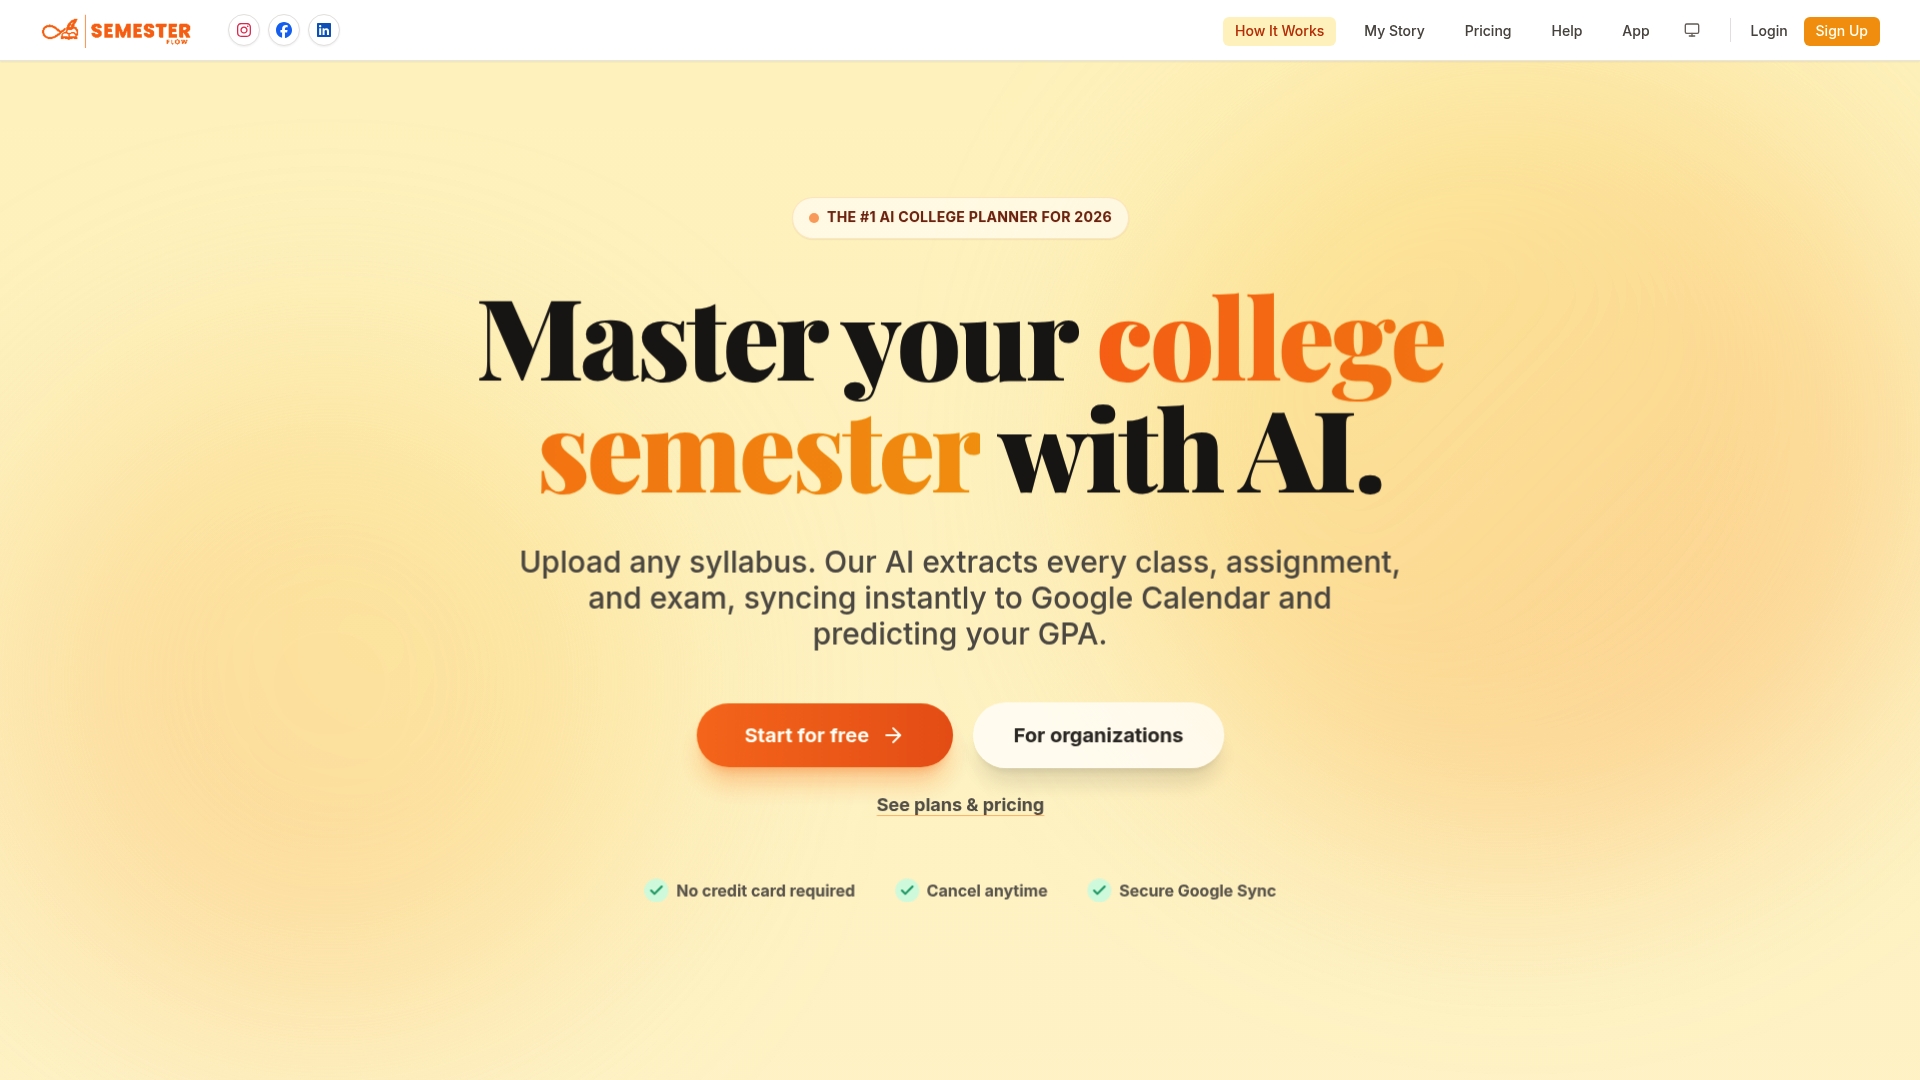
- We organize parsed syllabus data and documents directly within Google Drive structures.
- We sync extracted deadlines to Google Calendar automatically.
- We publish our security practices on our security and trust page for anyone evaluating how we handle uploaded files.
We don't replace admin-level sharing controls, and we're not trying to. We sit on top of them, reducing the manual work that leads to misplaced files in the first place. Check our pricing page to see the Pro plan at $7.99 per month, the Parent plan at $15 per month, or start with the Free Trial.
FAQ
How do I set sharing permissions on Google Drive?
Select the file or folder, click Share, then add people or groups and choose a role: Viewer, Commenter, or Editor. You can also adjust General access to control whether the link works for anyone outside your named list, as described in Google's official sharing guide.
Can someone access my Google Drive without my permission?
Not directly, but they can retain access you thought you removed if they belong to a group with separate permissions, or if a parent folder still grants them access. Testing effective access with a different account is the most reliable way to confirm what someone can actually see, per Google's explanation of how access is calculated.
Does Google Drive have family sharing?
Google Drive itself doesn't have a dedicated family sharing mode for personal accounts; sharing works the same way for any group of people through the Share dialog and folder permissions. Parents who want to monitor a student's academic progress separately from Drive sharing can use a tool like Semester Flow's Parent plan, billed at $15 per month.
Can anyone access a shared Google Drive link?
That depends entirely on the general-access setting attached to the link. A link set to Restricted only works for people already granted individual access, while a link set to a broader option like "Anyone with the link" works for anyone who has it, which is why Restricted is the safer default according to Google's guidance on stopping or changing sharing.
Sources
- Share files from Google Drive - Computer - Google Drive Help
- Manage sharing | Drive API | Google Developers